Anatomy of a Data Breach: How Companies Lose Your Information
Most breaches start with a stolen password, not a genius hacker. How intrusions unfold, where stolen data ends up, and the steps that actually protect you afterward.
The email arrives eleven months after the fact. We recently became aware of an incident that may have involved some of your information. Twelve months of free credit monitoring is being provided at no cost to you. There is a phone number nobody answers and a website that asks you to enter your last name and the last six digits of a number you do not have. A data breach almost never looks like the movie version, and the gap between the incident and that email is where most of the damage happens.
By the time you read that message, your details have usually been circulating for the better part of a year. Understanding why the gap is so long, and what happened during it, tells you a lot about what to do next.
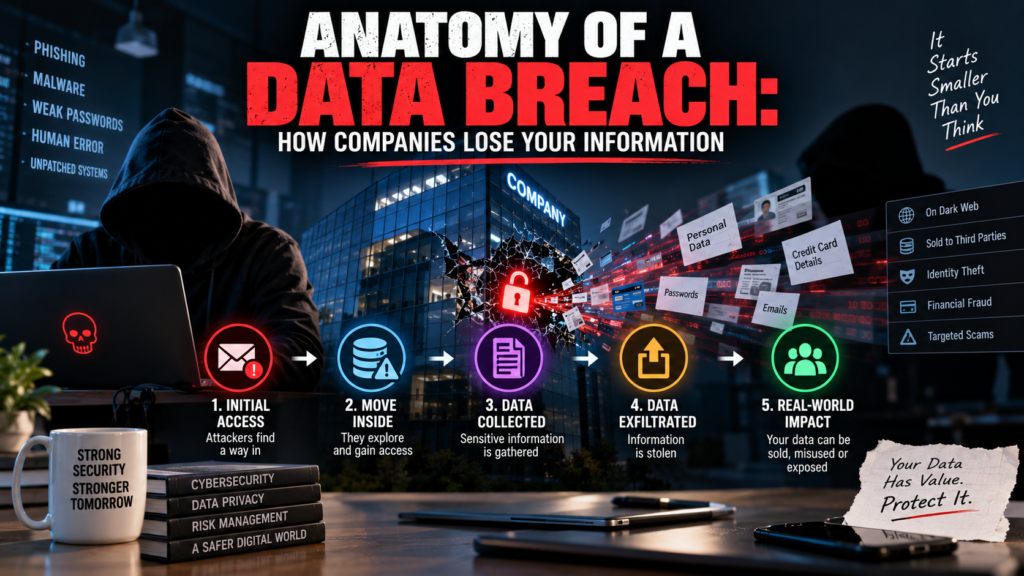
How a data breach actually starts
The mental image most people carry is wrong. Breaches are rarely a genius defeating sophisticated defenses. Security researchers who study incident patterns have found the same handful of entry points showing up year after year, and they are mostly boring.
Stolen credentials. The most common route. An employee reuses a work password on a personal site, that site gets breached, and the password ends up in a database attackers can search. Or an employee gets phished by a convincing email and types their credentials into a page that looks exactly like their company login. No exploit involved. Someone just logged in.
Unpatched software. A vulnerability is publicly disclosed and a fix is released. Organizations that apply it promptly are fine. Organizations with hundreds of systems and no complete inventory of what they run miss one, and attackers scan the internet continuously looking for exactly that.
Exposed storage. Cloud storage that was configured for public access when it should have been private. This has caused a remarkable number of incidents. It requires no attack at all, only somebody finding it.
Vendors. Companies grant access to payroll processors, marketing platforms, support software, and analytics providers. Each one is a path in. When a widely used vendor is compromised, every customer of that vendor is potentially affected at once, which is why some incidents seem to hit dozens of unrelated organizations in the same week.
Insiders. Less common than the others, but it happens, ranging from deliberate theft to someone downloading a customer list to a personal laptop before changing jobs.
The quiet middle part
Getting in is the beginning. What follows is the part that determines how bad it gets, and it typically unfolds over weeks or months.
An attacker who lands on one machine usually has limited access. So they look around. They map the network, find where the interesting systems are, and hunt for credentials with more privileges, often stored carelessly in scripts, configuration files, or shared documents. Then they move to a more valuable system and repeat.
This phase is slow and deliberately quiet. The goal is to look like normal activity, because most detection depends on noticing something unusual. An account that already exists, doing things that account is allowed to do, at reasonable hours, generates no alarm.
Then comes extraction. Data is copied out, often in small pieces over time, sometimes compressed and encrypted first, sometimes disguised as ordinary outbound traffic. Industry incident reports have consistently shown that the interval between initial compromise and detection is frequently measured in months, and that a substantial share of breaches are discovered not by the victim organization but by an outside party: a researcher, a payment processor noticing fraud patterns, or law enforcement.
That is the answer to why you find out so late. The company often found out late too.
Where your data goes next
Stolen data has a supply chain, and different types of information take different paths.
- Email and password combinations get compiled into large searchable collections and fed into automated tools that try them across thousands of sites. This is called credential stuffing and it is the reason password reuse is so dangerous.
- Payment card numbers have short useful lives, because banks cancel them once fraud appears. They get sold fast and used fast.
- Identity documents and government numbers hold value for years, because you cannot change them. These support loan fraud, tax fraud, and account opening long after the breach fades from the news.
- Detailed personal profiles combining name, address, employer, and security question answers are used for targeted social engineering. Someone who knows your bank, your recent purchase, and your mother’s maiden name is far more convincing on the phone.
There is a second wave people underestimate. Data from separate breaches gets combined. Your email from one, your phone number from another, your address from a third. The merged profile is more dangerous than any single source, and it explains why scam calls sometimes contain details that feel impossible for a stranger to know.
What to do when you get the notification
Practical sequence. Do these in order.
First, change the password on that account, and anywhere you reused it. Be honest about the reuse. If you used a variation, that counts, because attackers test variations. Use a password manager to generate genuinely different passwords, so you never have to do this exercise again.
Second, turn on two factor authentication on that account and on your email. Email first if you have to choose, since it can reset everything else. Authenticator apps are stronger than text messages.
Third, if identity documents or government identifiers were involved, freeze your credit. A freeze stops new accounts being opened in your name and is free to place and lift in many countries, including the United States. You do it with each major credit bureau separately. This is the strongest single protection available to an individual, and it is more useful than the free monitoring you were offered, because monitoring only tells you afterward.
Fourth, watch your accounts for the next several months, not the next week. Set up transaction alerts with your bank. Check statements. Fraud often arrives long after attention has moved on, which is partly the point.
Fifth, expect targeted scams. After a breach, people receive calls and emails that reference real details from the leaked data. The rule that protects you: never act on an inbound contact. Hang up, then call the number printed on your card or on the official website. Legitimate institutions have no problem with this.
What not to bother with
Do not click links in the breach notification email itself, since scam emails imitating breach notices are common. Go to the company site directly. And do not pay for identity protection services in a panic, since the freeze does most of the work for free.
Why this keeps happening
It is tempting to treat each breach as an individual failure, and sometimes it is. But the pattern is structural, and worth understanding if you want to make good decisions about who you give your data to.
Organizations collect far more than they need. Storage is cheap and data might be useful later, so the default is to keep everything indefinitely. A company that deleted records it no longer needed would have far less to lose, but nothing in most organizations rewards deletion.
Security spending competes with everything else and produces no visible return when it works. The manager who prevented a breach has nothing to show. The one who shipped a revenue feature has a number. Guess which budget grows.
And the costs land unevenly. When a company loses your data, the company faces regulatory penalties, legal costs, and reputational damage that often fades within a year. You face the possibility of fraudulent accounts in your name using information you cannot rotate. Your date of birth is permanent. Your government identifier is permanent. The mismatch between who bears the risk and who makes the decisions is the root of the problem, and it is why regulation, rather than better intentions, is what tends to change behavior.
Which leaves you with a straightforward if unsatisfying strategy: assume your information will end up somewhere it should not, and build the protections that make that outcome survivable. Unique passwords so one leak stays one leak. A second factor so a stolen password is not enough. A frozen credit file so your identity cannot be borrowed. Give out less where you have a choice, and treat any unsolicited contact that knows things about you as a warning sign rather than a reassurance.
Related reading
More on protecting yourself online: